Security Labs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.
Auditing the auditor: Unmasking Apex Accelerator
REF8801 exposes how Apex Accelerator combines convincing Web3 services with malicious npm packages, attacker-controlled AI infrastructure, and cross-platform malware delivery.
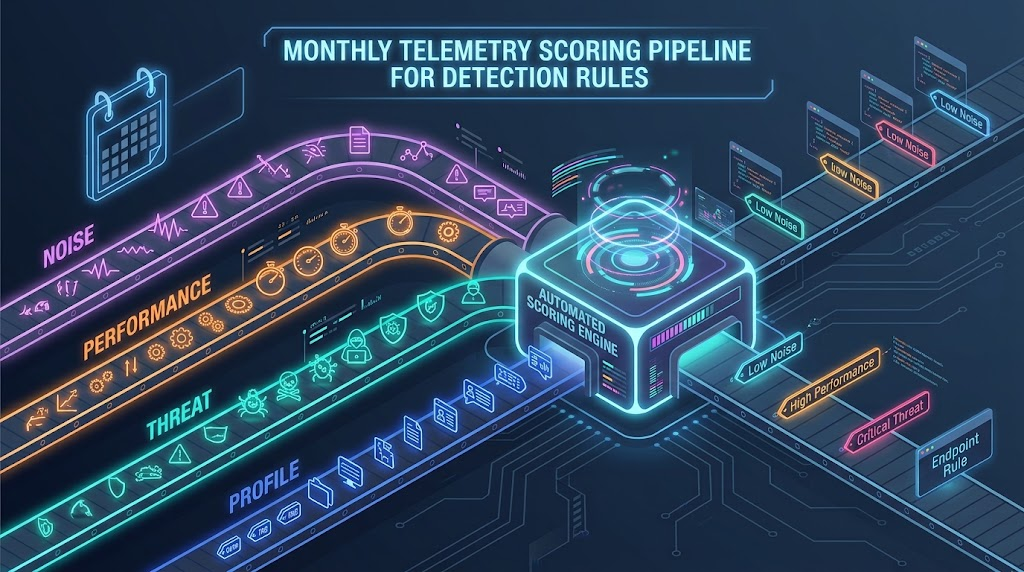
Behind the tags: How Elastic SIEM grades 1,781 detection rules on noise, speed, and threat coverage
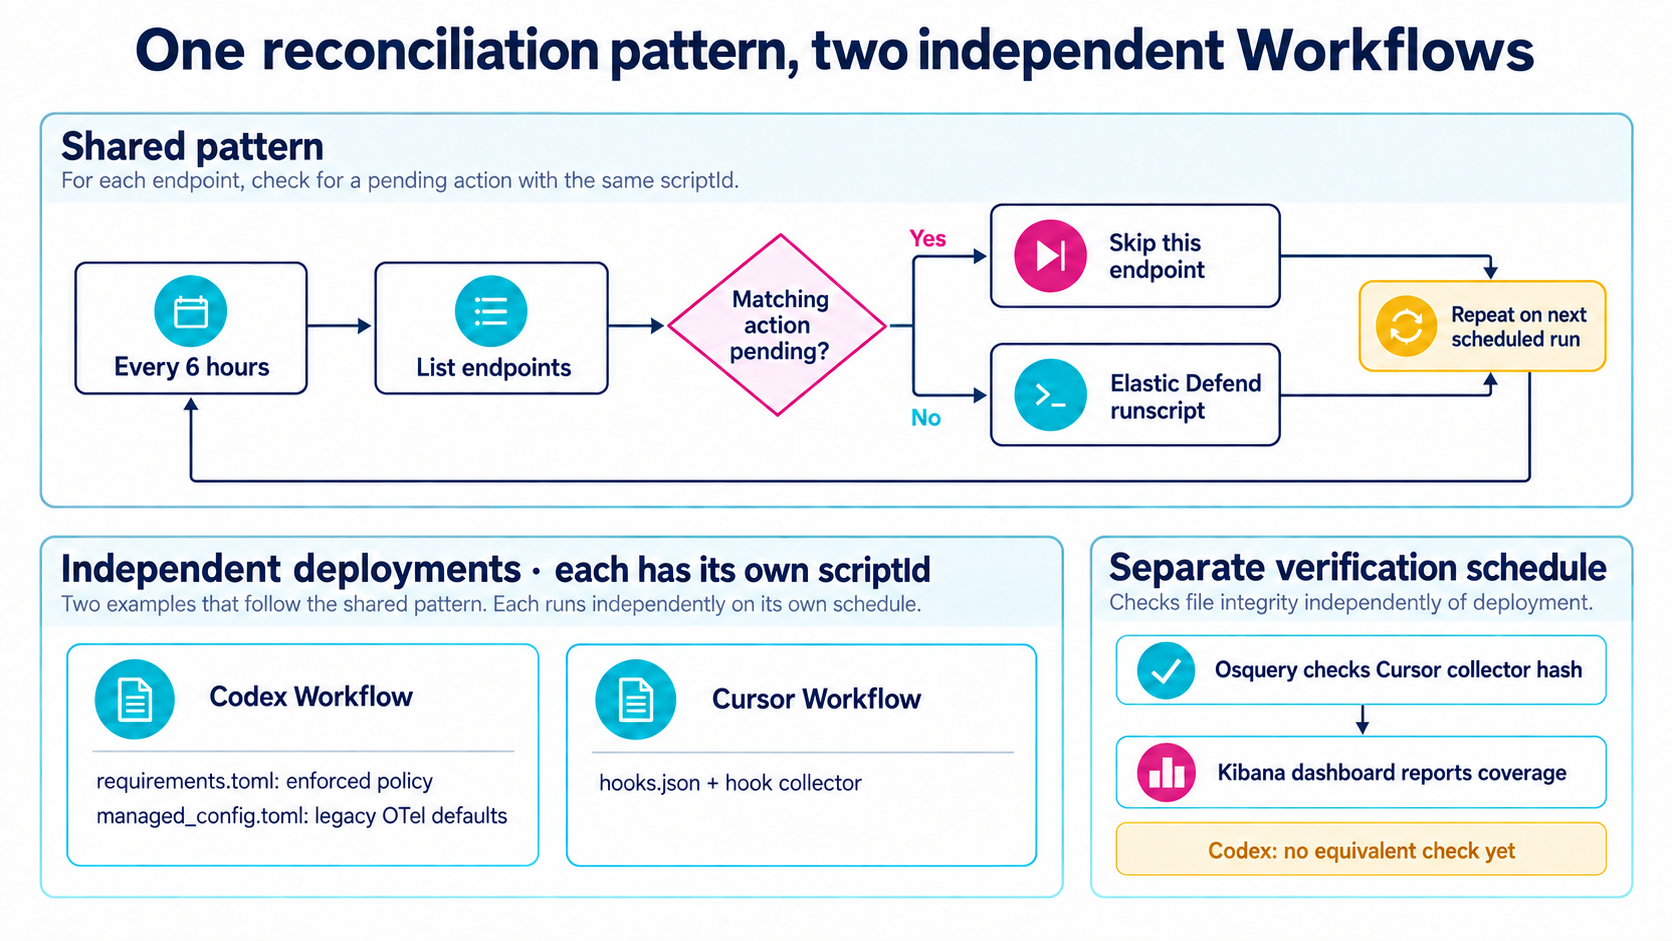
No MDM for Linux? A 68-line Elastic workflow keeps every endpoint's config current
Quarantined isn't contained: Agentic phishing response with Elastic and Sublime
Blog
Hand-picked stories from our editors — threat detection, audit logging, and security operations insights.
One SOC, 100 projects: running centralized alert triage on Elastic Security Serverless
We linked one Elastic Security project to 100 others and ran the full prebuilt detection catalog from the origin, with all the ingest landing in the linked projects. It held up, and where it deliberately does not reach is the interesting part.
Why 2026 is the Year to Upgrade to an Agentic AI SOC
Agentic AI SOCs differ from copilot-only models by autonomously prioritizing attacks over alerts, executing closed-loop containment, and providing traceable reasoning for every decision, allowing analysts to focus on high-value investigations.
Data access: the hidden cost of security vendor lock-in
Getting data into a security platform is always easy; getting it back out is where vendors add cost, extra tooling, and latency, and it is the part of the evaluation most teams overlook.
Not another Log4Shell: inside the Log4j 2 deserialization allowlist bypass
We reproduced this java deserialization vulnerability against official Log4j 2.26.1 JARs. Getting to command execution took two more things that Log4j itself does not ship. Here is how the bypass works, which versions carry it, and what to hunt for.
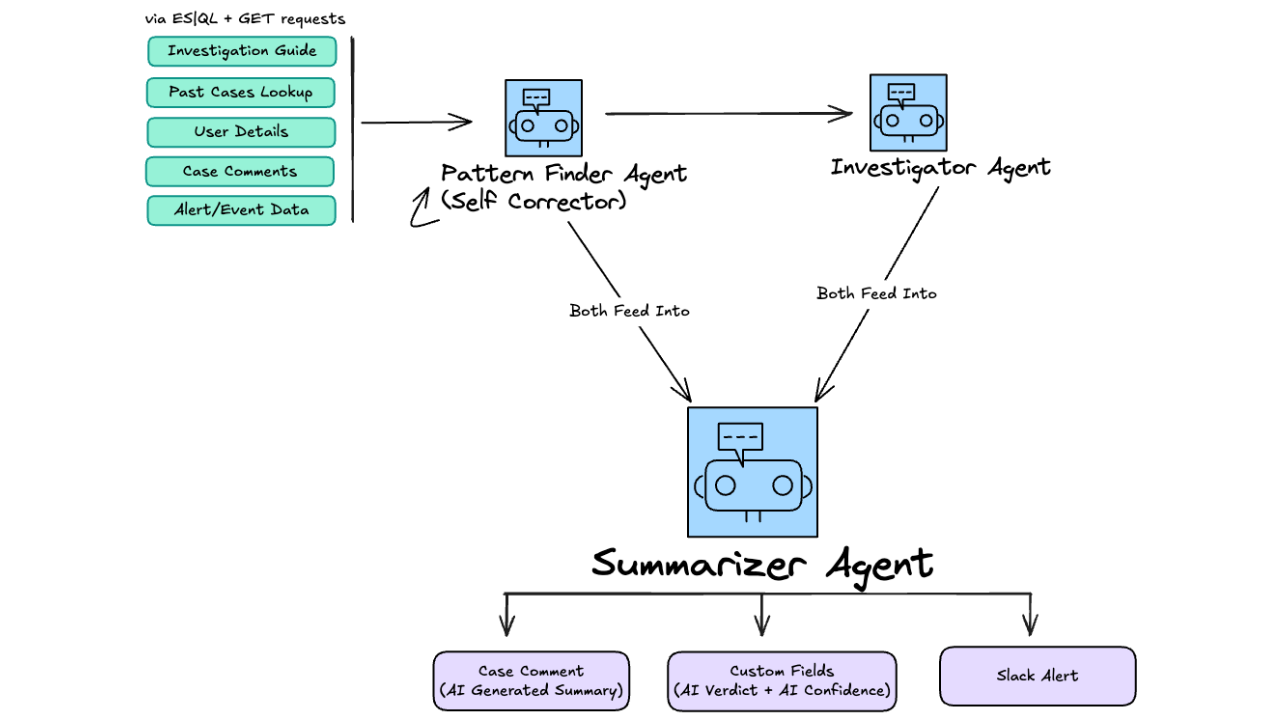
Inside Elastic's agentic SOC: How we took AI alert triage from 60% to 92% accuracy
Elastic's InfoSec team runs three agents that read the detection rule's investigation guide and the closure reasons on 30 days of past cases. Analysts now clear most alerts with a single click in Slack.
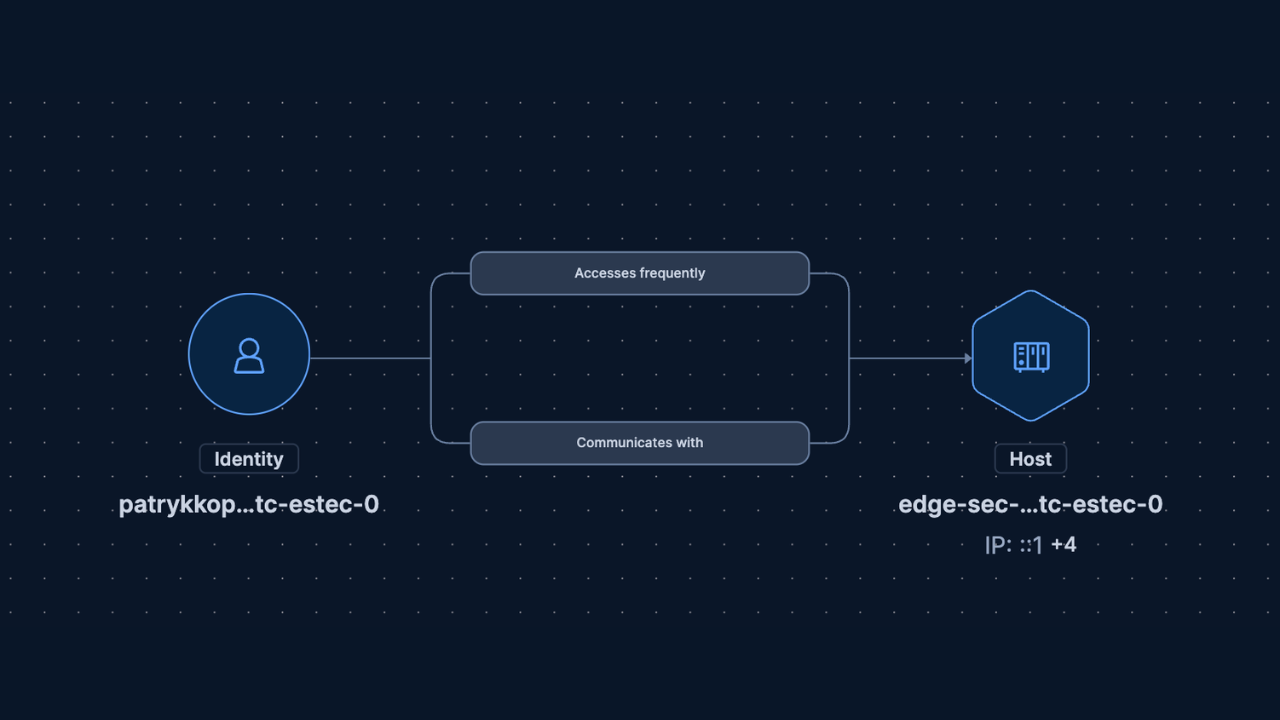
How a team of entity maintainers monitors, connects and scores entities in Elastic Security
Inside Elastic Security, background jobs called maintainers each own one piece of every user, host and service record, from building entities out of raw logs to resolving identities and scoring risk.
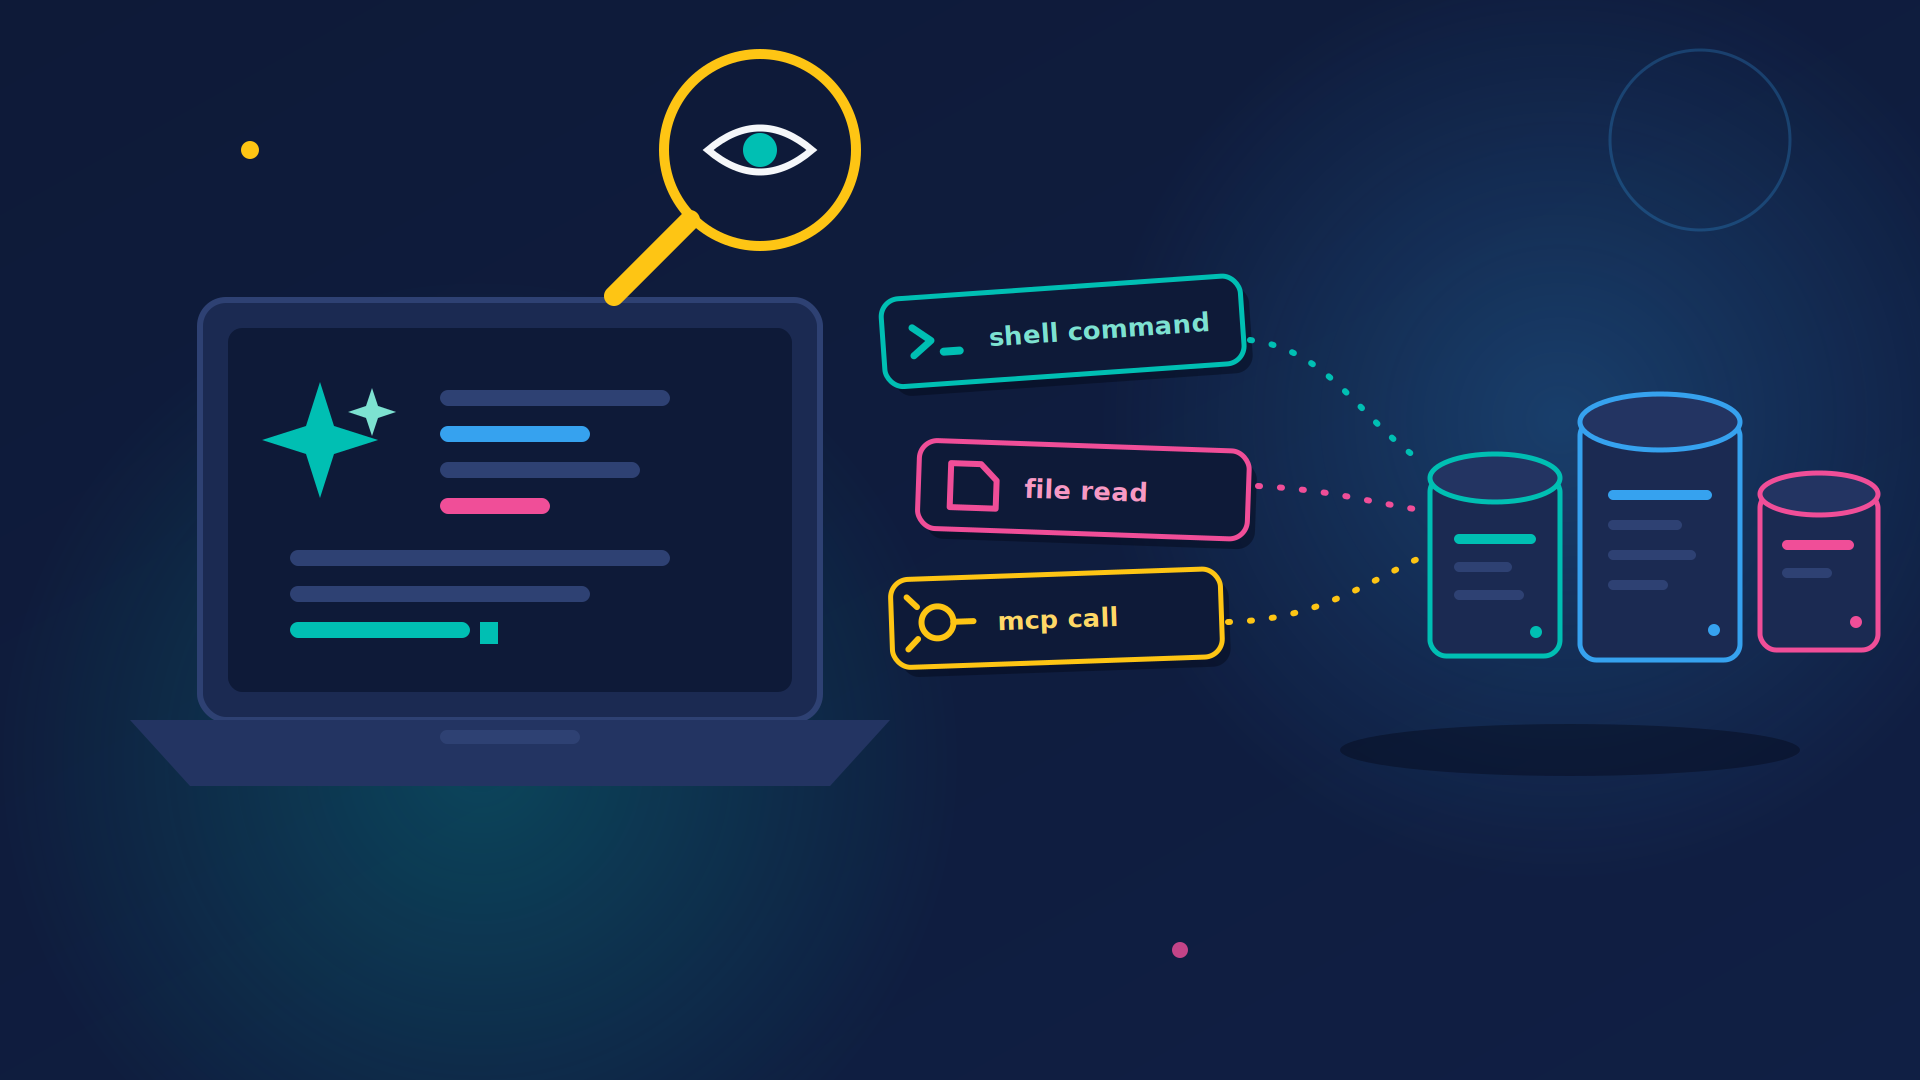
13 million tool calls: auditing every AI coding agent action with Elastic Agent
Cursor hooks and Elastic Agent capture every tool call, shell command, file read and MCP request as structured events you can hunt with ES|QL.
The security signal log tailing can't see: tracking npm cooldown removals with Elastic Agent
A 40-line CEL integration snapshots .npmrc files every 6 hours to catch cooldown removals. This post walks through the three ways we broke filestream before landing on snapshot semantics.
Benchmarking the Agentic SOC: How we evaluate LLMs for security workflows
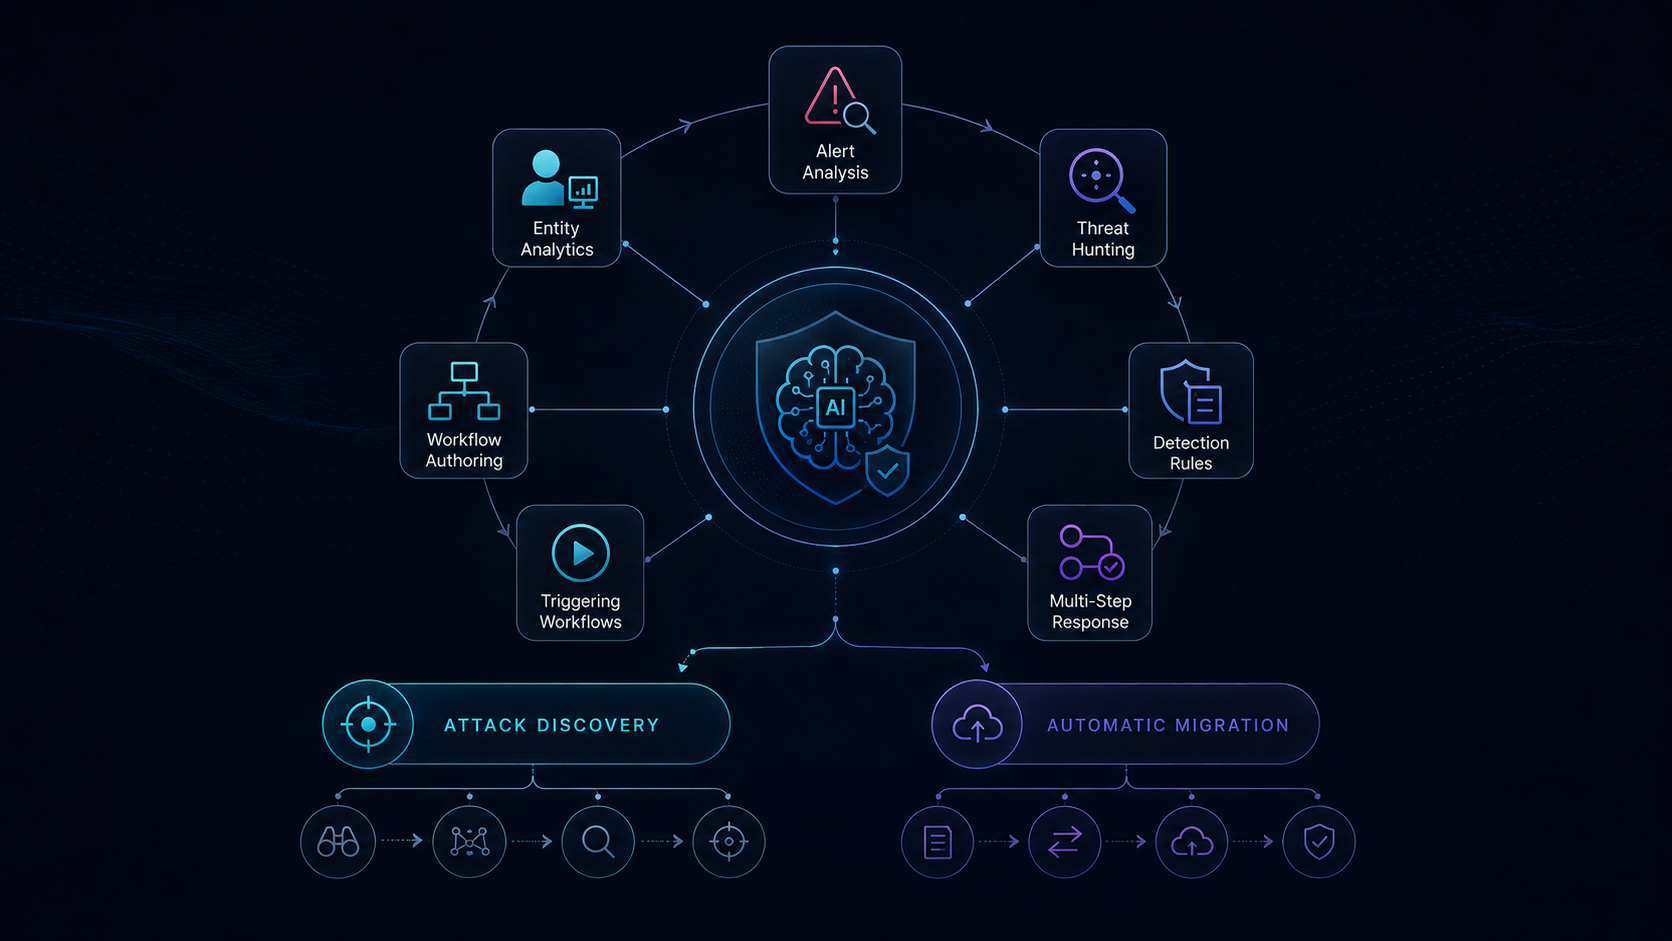
Public leaderboards can't tell you which LLM to trust in your SOC, so Elastic built an evaluation framework that grades models on the work (tool calls, execution traces, blind judging) across Agent Builder, Attack Discovery, and automatic migration.
Agents vs. agents: how we triage HackerOne reports for $2 each, 85% as well as a human
LLMs made it cheap to flood bug bounty programs with submissions. Here's how Elastic built an AI triage agent that matches human decisions 85% of the time, including the architecture, threat model and calibration against 3,300 real reports
SOC case management and detection rule history in Elastic Security
Elastic Security now tracks every detection rule change with one-click rollback and makes case data queryable out of the box, so SOC teams get audit trails and reporting without configuring anything.
Elastic goes all-in on Hacker Summer Camp at Black Hat and DEF CON in Las Vegas
Attack Discovery turns raw alerts into validated threats and Elastic Defend closes vulnerable driver gaps as fast as they're disclosed. Watch it all run against real attacks at the booth.
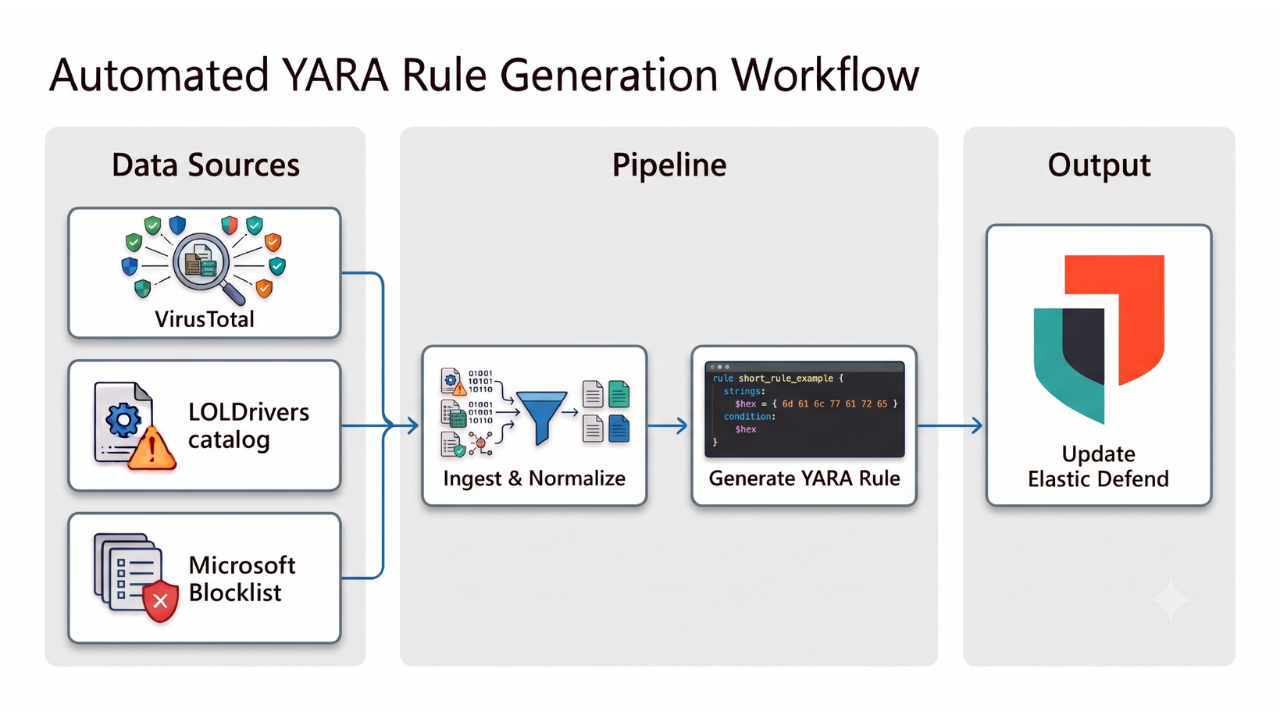
What's new in Elastic Defend: 800+ vulnerable driver rules, automated troubleshooting, and ARM support
Elastic Defend automatically generates and instantly deploys vulnerable driver YARA rules from VirusTotal, LOLDrivers and Microsoft's blocklist, closing the gap BYOVD attacks depend on. Plus a new troubleshooting skill and ARM endpoint protection.
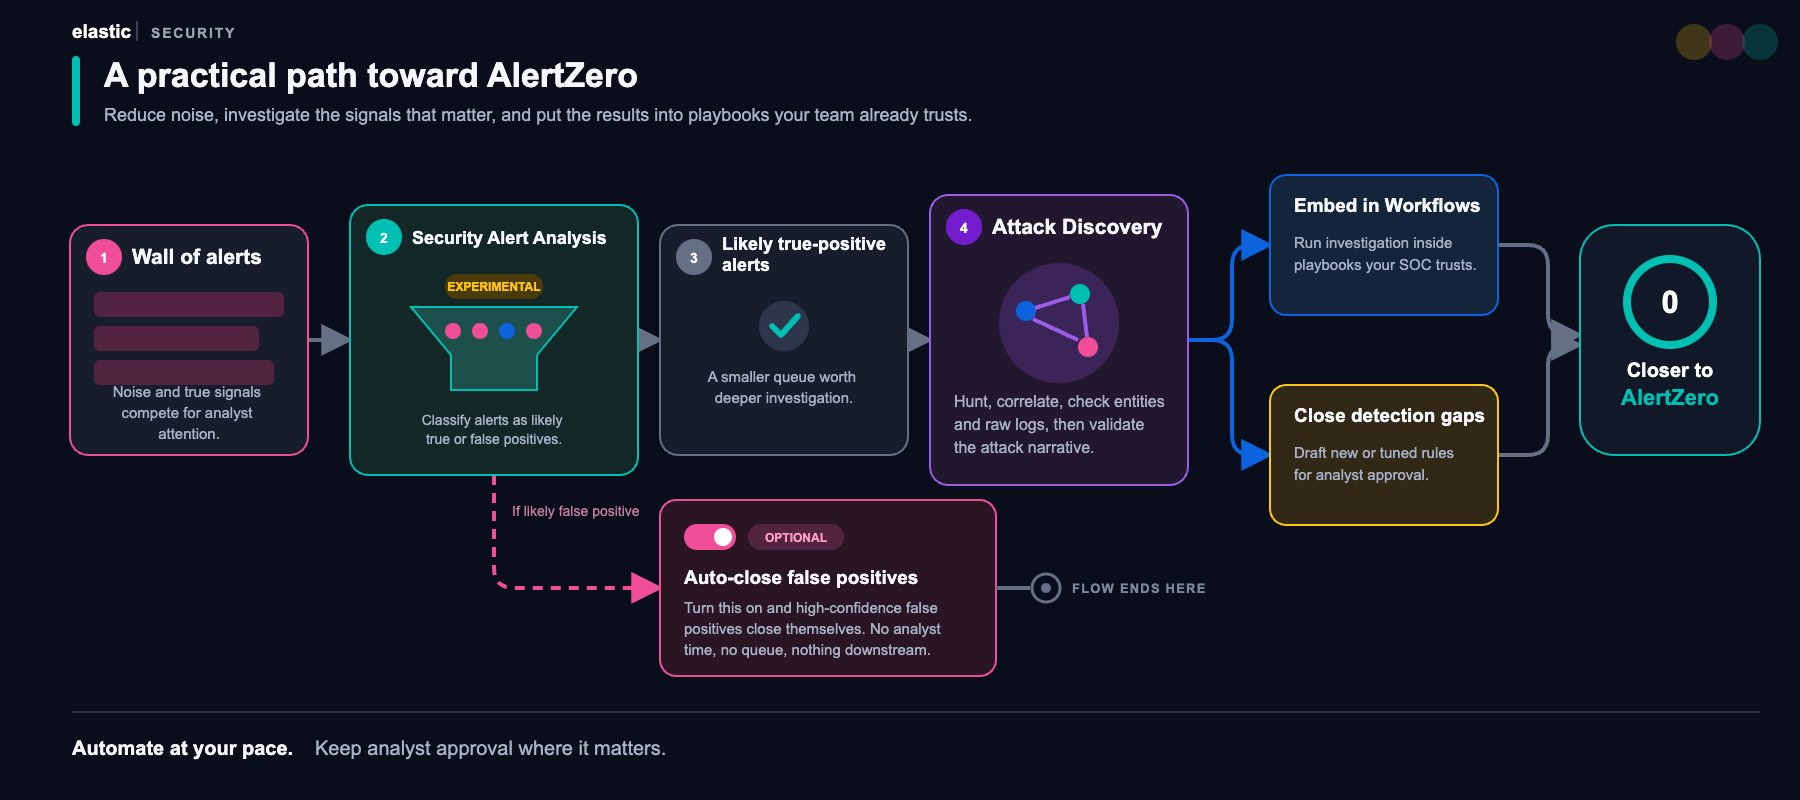
Journey to AlertZero: AI-driven alert triage and attack investigation for the agentic SOC
Elastic Security 9.5 gives SOC teams AI that handles first-pass alert triage and investigation, so analysts can get back to threat hunting and detection engineering instead of working through queue noise.
Stop rewriting detection rules by hand: automatic Sentinel-to-Elastic migration is here
Elastic's first automatic migration from a modern SIEM. Translate your Sentinel detection rules into Elastic Security without rebuilding them.